Here are some of the top Cybersecurity news articles for the past week:
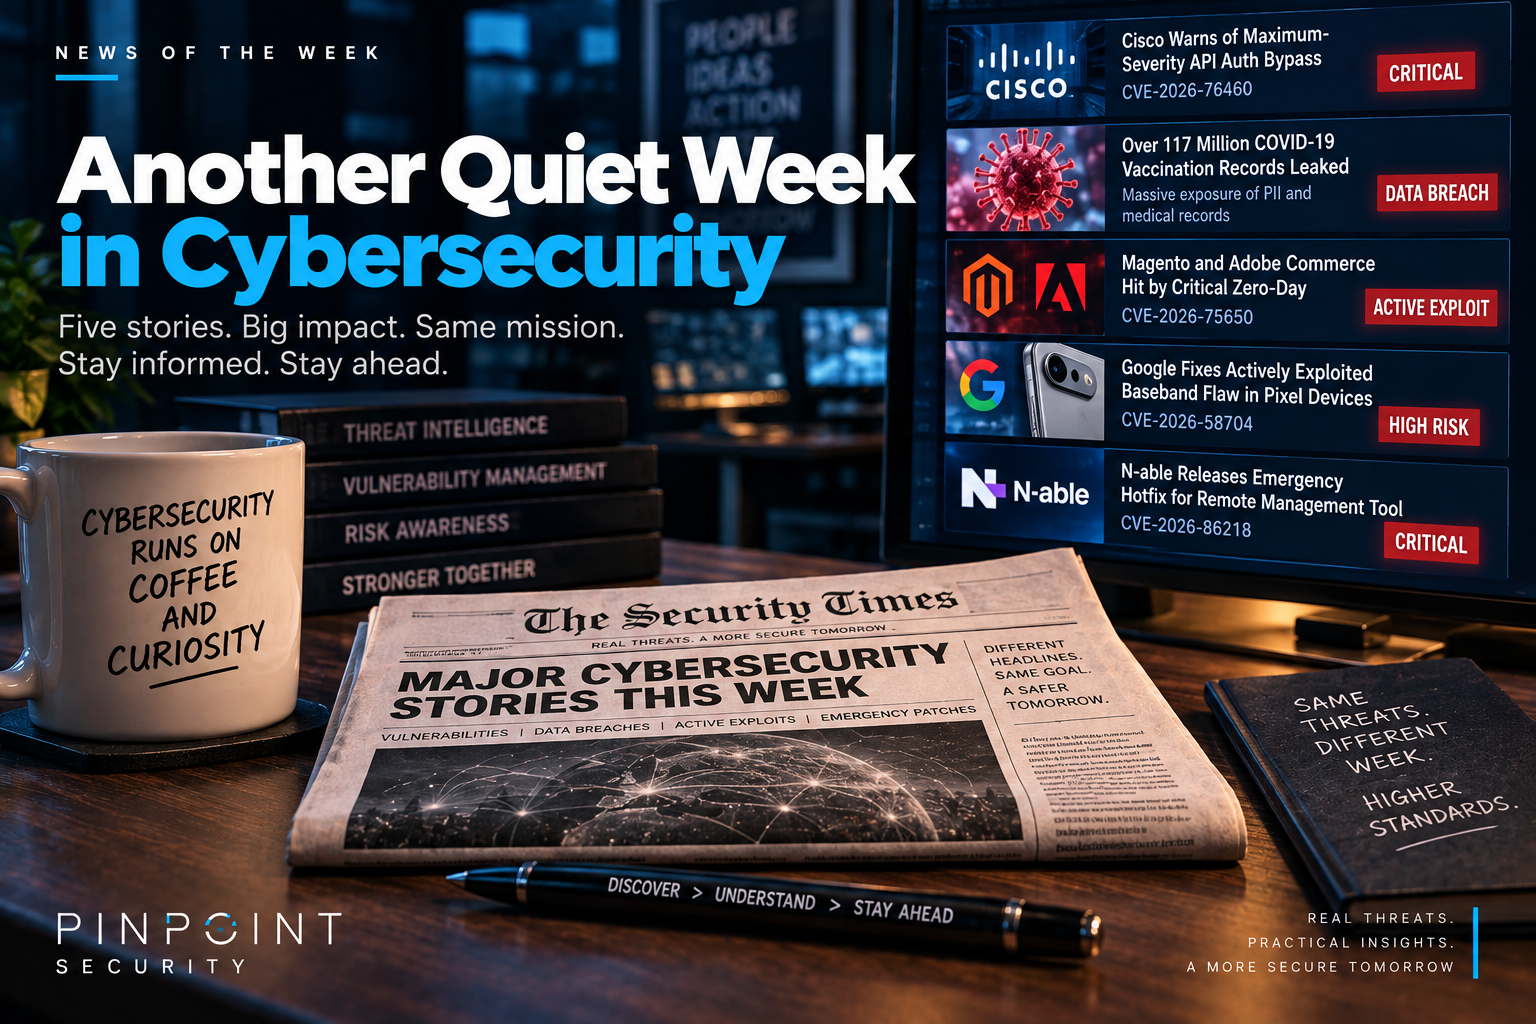
🚨 Cisco Warns of Maximum-Severity API Auth Bypass (CVE-2026-76460)
Cisco issued an urgent advisory for a critical flaw affecting its Identity Services Engine (ISE) and ISE Passive Identity Connector (ISE-PIC). Carrying a CVSS score of 10.0, the vulnerability stems from insufficient authentication controls on an API endpoint, allowing unauthenticated remote attackers to bypass web management interfaces and execute commands with full root privileges. Active exploitation has already been confirmed in the wild.
🔓 Over 117 Million COVID-19 Vaccination Records Leaked
A massive health data breach resulted in the exposure of over 117 million Chinese COVID-19 vaccination records. The leaked database contained extensive personally identifiable information (PII) alongside medical track records, highlighting ongoing risks surrounding the long-term storage and access controls of large-scale public health databases.
⚠️ Magento and Adobe Commerce Hit by Critical Zero-Day (CVE-2026-75650)
Security researchers identified fast-moving exploitation of a maximum-severity flaw in Adobe Commerce and Magento Open Source. Discovered under active weaponization shortly after exposure, the vulnerability allows remote attackers to bypass security layers and execute arbitrary code on vulnerable e-commerce platforms, prompting urgent patching calls for online retailers.
📱 Google Fixes Actively Exploited Baseband Flaw in Pixel Devices
Google confirmed targeted exploitation of CVE-2026-58704, a high-severity privilege escalation flaw located within the Google Pixel modem subcomponent. The vulnerability allows an attacker within radio proximity to escalate privileges without requiring user interaction, creating high risks for stealthy baseband-level exploits.
🛠️ N-able Releases Emergency Hotfix for Remote Management Tool
Managed Service Provider (MSP) tooling vendor N-able deployed an emergency patch for its N-central Remote Monitoring and Management (RMM) platform. The unauthenticated remote code execution vulnerability (CVE-2026-86218) carries a CVSS score of 10.0, posing severe supply-chain risks for IT administrators and downstream clients if left unaddressed.