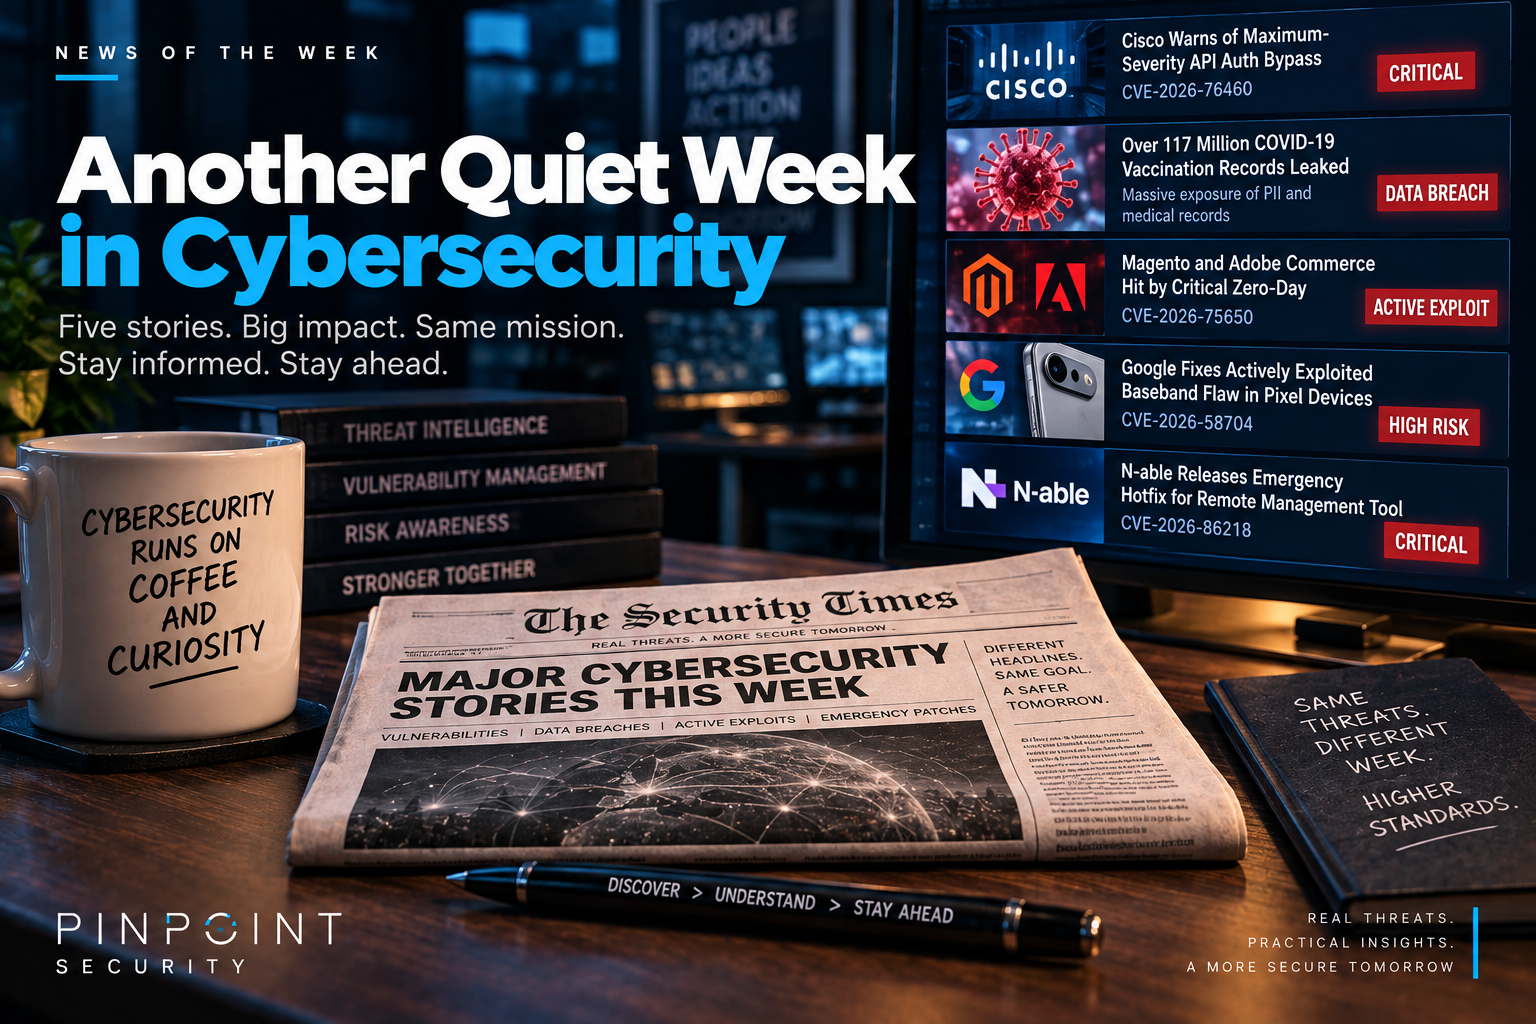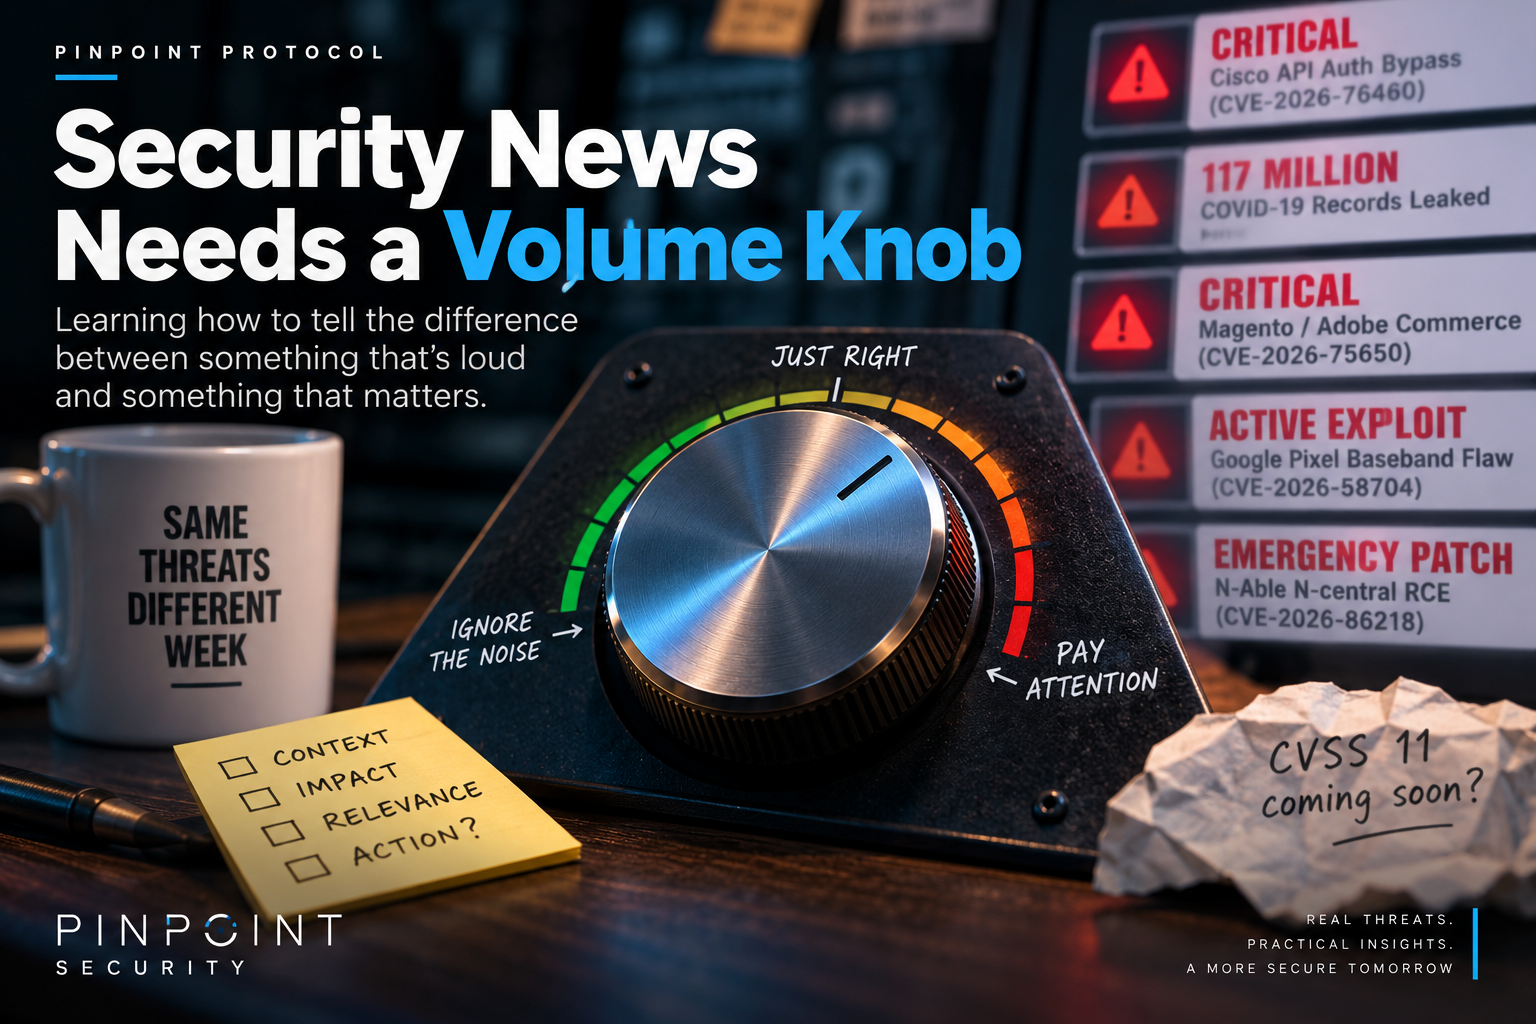
Like you all, I spend a fair amount of time reading Security news, and lately I’ve noticed that cybersecurity apparently has two volume settings: normal and VERY LOUD. This week alone brought us a maximum-severity Cisco vulnerability being actively exploited, a critical Adobe Commerce flaw, an emergency N-able hotfix, another actively exploited vulnerability affecting mobile devices, and news of a breach involving more than 100 million records. At some point, you start wondering whether CVSS is going to need an 11 😂 Joking aside, there is a real problem buried in all that urgency. When almost every week includes something described as critical, actively exploited, maximum severity, emergency, or zero-day, it’s surprisingly easy for those words to start losing their impact. I don’t think that’s necessarily a sign that we’re becoming careless. Humans naturally learn to filter information when they’re exposed to enough of it, and Security professionals have more information competing for their attention than ever. Vulnerability scanners, vendor advisories, threat intelligence, Security tools, news feeds, and internal alerts are all trying to tell us what matters. The skill is learning how to adjust the volume without muting it. Cisco’s ISE vulnerability is a good example of something that deserves to be turned up. It’s remotely exploitable without authentication, can lead to root-level command execution, and has been exploited in the wild. Those details tell me considerably more than the number 10.0 by itself. The same thinking applies to N-able’s N-central vulnerability. Remote monitoring and management platforms are particularly interesting from a Security perspective because of the access they’re designed to have. A pre-authentication remote-code-execution vulnerability in that kind of system deserves attention because understanding what the technology does gives us context for what compromise could mean. That’s something I’ve learned to appreciate more over time. Reading Security news effectively isn’t really about remembering every CVE number or reacting to whichever headline uses the strongest language. It’s about becoming curious enough to keep reading past the headline. Sometimes a vulnerability with a frightening score doesn’t affect anything you operate. Another issue with a less dramatic headline might involve a system sitting directly in an important attack path. A large data breach can teach us something entirely different about how information is stored and protected long after it was originally collected. Context changes the volume. I think that’s an important skill to develop because the amount of Security information we’re receiving isn’t going to decrease. We’re going to continue seeing newly discovered vulnerabilities, active exploitation, emergency patches, breaches, and plenty of headlines designed to make sure we click on them. Becoming numb to all of it isn’t the answer, but neither is treating everything like a five-alarm fire. The better approach is to stay curious. Read a little further. Understand what the affected technology actually does and where it exists in your environment. Learn what an attacker needs to take advantage of the issue and what successful exploitation would give them. Over time, those questions become less of a checklist and more of an instinct. You start developing your own internal volume knob. And that’s one of the things I enjoy about working in Security. There’s always something new to learn, but experience helps you figure out which things deserve your attention first…just don’t turn the volume all the way down 😉